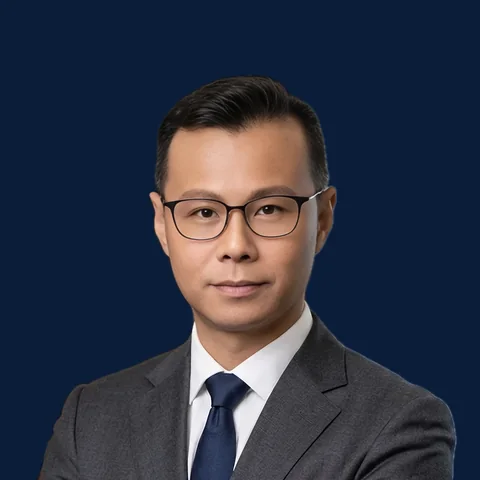
Terence Kok
Executive Director, AI Governance & Assurance Practice, Orion Five Engineering
Leads the AI governance and assurance practice and builds the working systems the toolkit is drawn from.
For heads of risk, compliance and internal audit
The Governed Enterprise Toolkit gives you the charter, policies, AI inventory, risk tiers and controls to stand up governance in about 90 days. It is the method behind our book, The Governed Enterprise, written down as Word and Excel files, with a portal where your registers, gap assessment and audit evidence live as records with owners, due dates and history.
Executive Director, AI Governance & Assurance Practice, Orion Five Engineering
Leads the AI governance and assurance practice and builds the working systems the toolkit is drawn from.
Founder and Director, SENSE Collective
Co-author of The Governed Enterprise with Terence, and co-creator of this toolkit. Read what they have written together.
Staff are already using AI tools. Vendors are adding agents to products you already run. Your board wants a position, and your auditor will ask for evidence. Most organisations start with a blank page and spend months writing documents that a regulator or certifier will then ask to see.
The free tools on this site tell you where you stand. This toolkit gives you the documents to close the gaps.
The modules build on each other. Each one produces the input the next one needs.
 1Governance foundation
 2Policies
 3Inventory and risk
 4Controls
 5Agentic and third-party risk
 6Operational risk integration
The charter, the committee that runs it, the decision rights behind it and a 90-day plan to stand it up.
 Word: Module 1 guideWord: AI Governance CharterWord: AI Governance Committee Terms of Reference
 Excel: RACI and decision rightsExcel: 90-day programme planWord: Worked Example: Standing Up Governance
You finish with An approved charter, a constituted committee and a dated plan.
A short top-level AI policy and four standards beneath it: acceptable use, agent autonomy, third-party AI and data handling.
Word: Module 2 guideWord: AI PolicyWord: Acceptable Use StandardWord: Agent Autonomy StandardWord: Third-Party AI StandardWord: AI Data Handling StandardWord: Worked Example: A Request to Use an AI ToolYou finish with A policy suite ready for tailoring and approval.
An AI system register, a tiering method, an agent risk matrix and an impact assessment template.
Word: Building the AI inventoryExcel: AI System RegisterWord: Risk Tiering GuideExcel: Risk Tiering WorksheetExcel: Agent Risk MatrixWord: AI Impact AssessmentWord: Worked Example: Tiering Three AI SystemsYou finish with Every AI system and agent listed, tiered and owned.
A control library with agentic controls, a regulatory crosswalk (ISO/IEC 42001, MAS, IMDA, OCC, HKMA), a Statement of Applicability, a gap assessment and an evidence checklist.
Word: Running a control self-assessmentExcel: AI Control LibraryExcel: ISO/IEC 42001 Statement of ApplicabilityExcel: Gap AssessmentExcel: Evidence ChecklistExcel: Regulatory CrosswalkWord: Worked Example: Scoring a Gap AssessmentYou finish with A scored gap assessment and an audit-ready evidence trail.
An onboarding gate for AI agents, an agent registry, supplier due diligence for models, MCP servers and skills, contract clauses and a stop-and-incident runbook.
Word: Module 5 guideExcel: Agent Onboarding GateExcel: Agent Registry and Know Your AgentExcel: Third-Party and Supply-Chain Due DiligenceWord: Third-Party AI Contract ClausesWord: Worked Example: From Supplier Answers to Contract ClausesWord: Agent Stop and Incident RunbookWord: Worked Example: Taking an Agent Through the Onboarding GateYou finish with Every agent gated before go-live, every supplier assessed, and a tested way to stop an agent.
An RCSA for AI agents, a key risk indicator register, a scenario library and test log, an issues and risk acceptance register, and a roadmap to the MAS dates.
Word: Module 6 guideExcel: Risk and Control Self-Assessment for AI AgentsExcel: Key Risk Indicator RegisterExcel: Scenario Library and Test LogExcel: Issues and Risk Acceptance RegisterExcel: Roadmap, Maturity and Value by TierWord: Worked Example: Risk, Indicators and Acceptance for an AgentYou finish with Agentic risk reported through the operational risk process you already run.
The files give you the method. The portal keeps your own records, so they stay current and an auditor can trust them.
The AI System Register, agent registry, control assessment and operational risk register are live records. Each has a named owner, a review date, a status and a history of every change.
Every control scored below its target gets an action with an owner and a due date. Overdue actions appear in your weekly reminder and your calendar.
When a regulator changes a rule, the controls it touches are flagged for you to re-confirm, with a suggested redline and the documents it affects.
Each template has a change log and a clause-level comparison, so you can see what changed between versions and why.
The quarterly paper is built from your registers, gap scores and risk indicators, and saved as a dated PDF with a checksum, kept as evidence.
Attach evidence to a control, have a second person sign it off, and export a pack for your certification body or internal audit. The pack carries checksums but is not signed or certified, and it supports an audit rather than replacing one.
A new agent goes through a request and a second-person approval before it joins the register. Exceptions and risk acceptances carry an expiry and a reminder.
A readiness score tracks you through the 90 days. Once at least five licensees have scored, you also see where you stand against them, anonymised.
The live registers are switched on for your licence when you are onboarded. Your records are kept separately for each licence and are not visible to other licensees. Read the data privacy statement.
Mapped to the standard's clauses and Annex A, with a Statement of Applicability template to complete.
Controls tagged to Govern, Map, Measure and Manage.
Risk tiers and deployer duties referenced at article level, where the requirement is clear.
Cross-references to the MAS AI risk management guidance and the IMDA model governance frameworks.
Choose a step to see the files you use in it.
Word: Module 1 guideWord: AI Governance CharterWord: AI Governance Committee Terms of ReferenceExcel: RACI and decision rightsExcel: 90-day programme planWord: Worked Example: Standing Up GovernanceWord: Module 2 guideWord: AI PolicyWord: Acceptable Use StandardWord: Agent Autonomy StandardWord: Third-Party AI StandardWord: AI Data Handling StandardWord: Worked Example: A Request to Use an AI ToolWord: Building the AI inventoryExcel: AI System RegisterWord: Risk Tiering GuideExcel: Risk Tiering WorksheetExcel: Agent Risk MatrixWord: AI Impact AssessmentWord: Worked Example: Tiering Three AI SystemsWord: Module 5 guideExcel: Agent Onboarding GateExcel: Agent Registry and Know Your AgentExcel: Third-Party and Supply-Chain Due DiligenceWord: Third-Party AI Contract ClausesWord: Worked Example: From Supplier Answers to Contract ClausesWord: Agent Stop and Incident RunbookWord: Worked Example: Taking an Agent Through the Onboarding GateWord: Running a control self-assessmentExcel: AI Control LibraryExcel: ISO/IEC 42001 Statement of ApplicabilityExcel: Gap AssessmentExcel: Evidence ChecklistExcel: Regulatory CrosswalkWord: Worked Example: Scoring a Gap AssessmentWord: Module 6 guideExcel: Risk and Control Self-Assessment for AI AgentsExcel: Key Risk Indicator RegisterExcel: Scenario Library and Test LogExcel: Issues and Risk Acceptance RegisterExcel: Roadmap, Maturity and Value by TierWord: Worked Example: Risk, Indicators and Acceptance for an AgentRules move faster than documents. Licensed users get a governance radar inside the library: a weekly scan of new AI frameworks, laws, regulations, standards and supervisory guidance across the EU, the US, the UK, Singapore and ASEAN, Hong Kong, China, Japan, Korea, India and the international bodies.
One named user, with their own sign-in. For consultants, independent advisers and heads of function who run the programme themselves.
Request an individual licenceA stated number of named seats under one licence, for a risk, compliance and audit team. Seats can be reassigned when people move.
Request a team licenceI agree the licence with you by email, so it fits your team. Tell me about your organisation below and I will reply personally.
I read every request myself and reply within two working days. There is no obligation, and no payment is taken on this form.
I use your details only to reply to this request. See the data privacy statement.
Microsoft Word for documents and Microsoft Excel for registers, matrices and assessments. Everything is editable. The spreadsheets use drop-downs and formulas, so scores and counts update as you fill them in.
Yes. The files are yours to adapt for your organisation. Each one carries a licence line in the footer with your organisation name and licence number. Please leave that line in place.
Yes, for named client engagements. Advisers such as law firms, consultants and auditors may translate and adapt the files and give the adapted documents to clients as part of their paid work, as long as the licence line stays in the footer and the Toolkit is credited. The files may not be resold or published as a product, or placed where others can download them. Everyone at your firm who works with the files needs a seat on the licence.
An individual licence is for one named person. A team or organisation licence covers a stated number of named seats, each with its own sign-in.
With an emailed link. There are no passwords to set or forget. Enter your email, and a single-use link arrives that works for 15 minutes.
Yes. Standards and regulation move, and the library is versioned. Each template has a change log and a clause-level comparison, and licensed users are told when files are updated. The governance radar flags the controls a regulatory change touches.
Yes. Every register and assessment is also a spreadsheet, and you can import and export your records as CSV. The portal adds owners, due dates, history and evidence that a spreadsheet emailed between people cannot give an auditor.
Seven: ISO/IEC 42001, NIST AI RMF, the EU AI Act, MAS (Guidelines on AI Risk Management), IMDA (model governance frameworks), OCC (Bulletin 2026-54) and the HKMA discussion paper. ISO and NIST are standards rather than regulators. The mappings are the authors' reading and indicative, so confirm them against the primary texts. Sector packs for banking, insurance, healthcare and the public sector add further references.
Your records are stored per licence and are not shown to other licensees. The benchmark uses scores only, and only once at least five licensees have one. The assistants that answer questions or review a policy send the text you give them to an AI provider to produce the reply. The tailoring assistant stays off for your licence until you ask for it. The full statement is on the data privacy page, and hosting, sub-processors and security controls, including what is not there yet, are on the trust and security page.
Yes. Licensees can book office hours and quarterly briefings from inside the library, and send a question that is answered by email.
No. The documents are templates for your legal, risk and compliance teams to review and adopt. They do not replace advice on your own obligations.