Executive Summary
The most dangerous way generative AI fails is with a confident, incomplete answer. A crash does less harm. In safety domains like AEC, where results must be deterministic, that makes probabilistic AI unfit for direct use in safety-critical decisions. Liability for its outputs falls entirely on the firm that deploys it, never on the system.
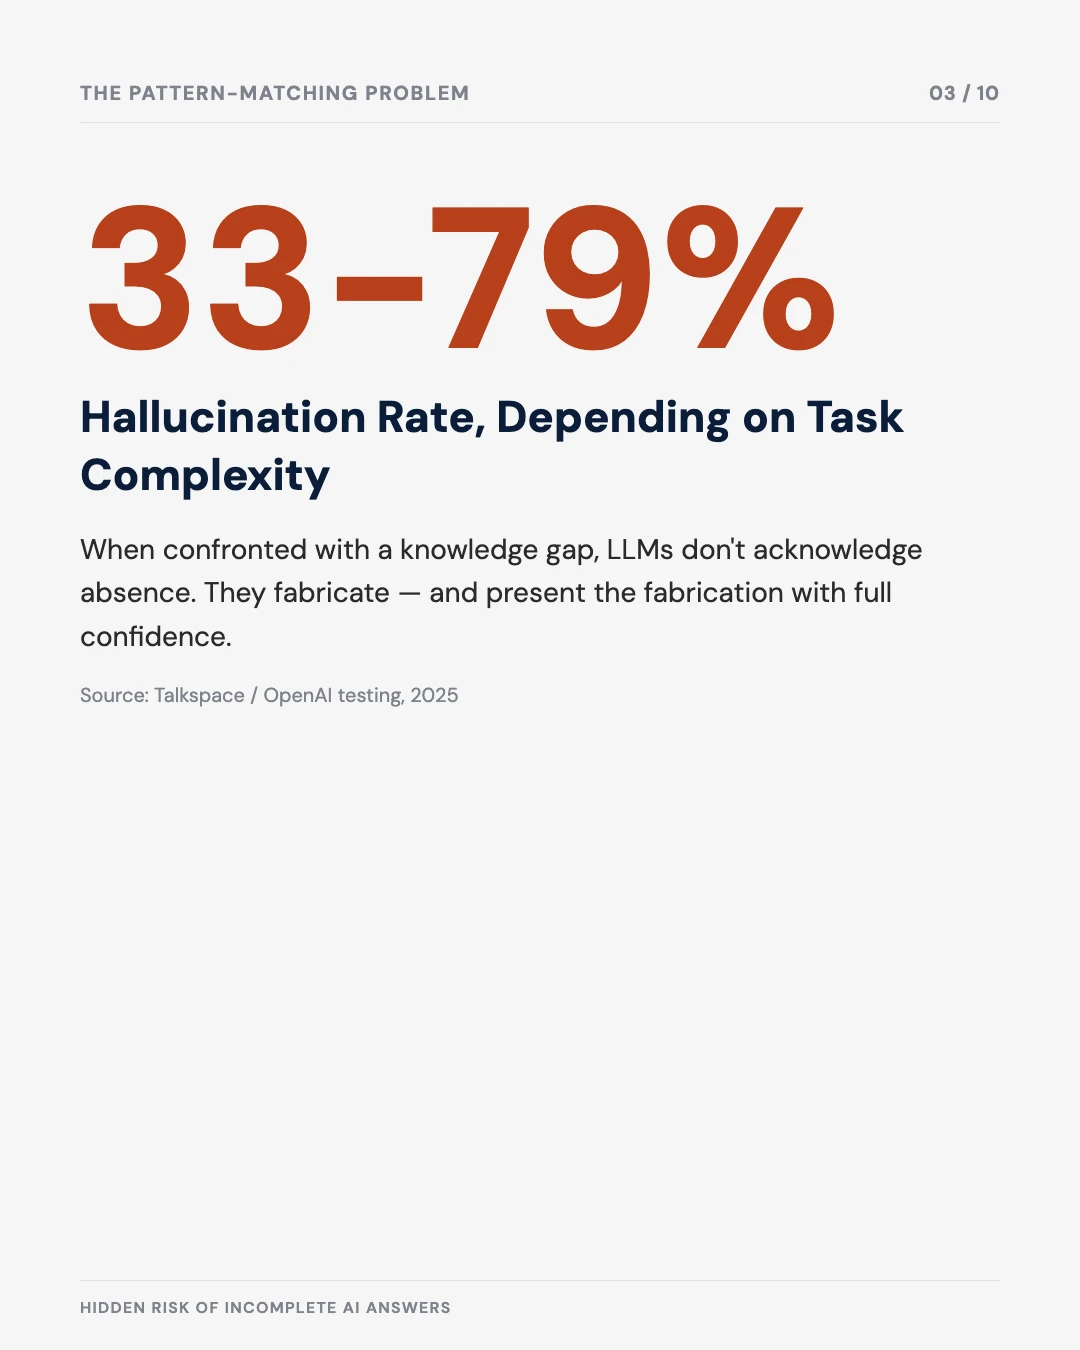
33-79%
hallucination rate OpenAI itself measured on its own reasoning models, depending on the benchmark
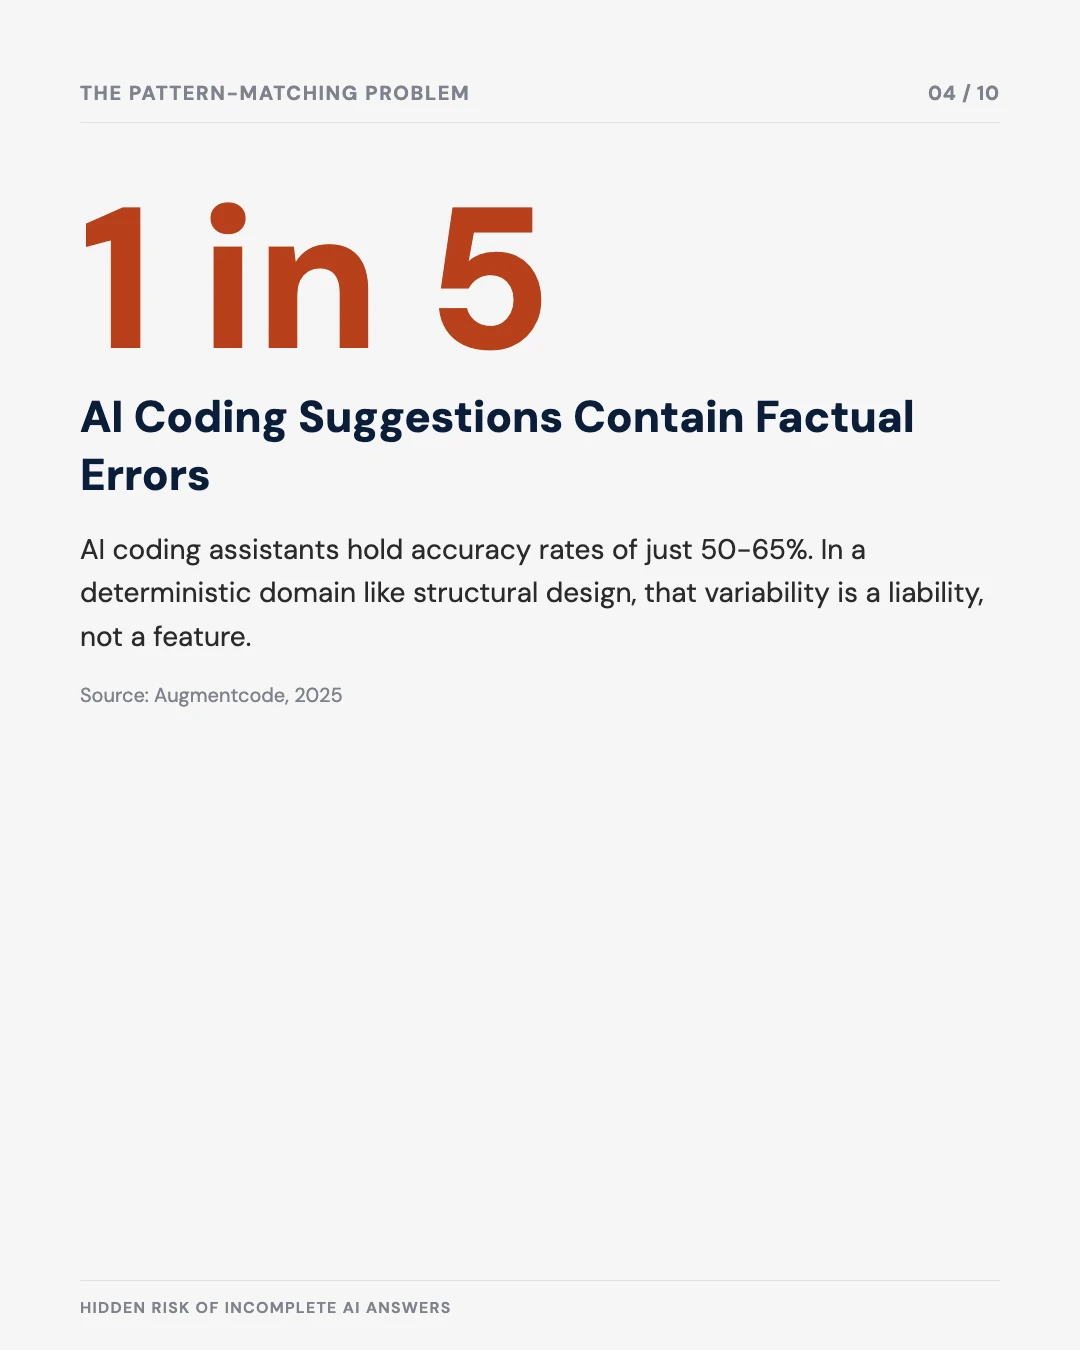
1 in 5
AI coding suggestions contain factual errors, even at 50-65% headline accuracy
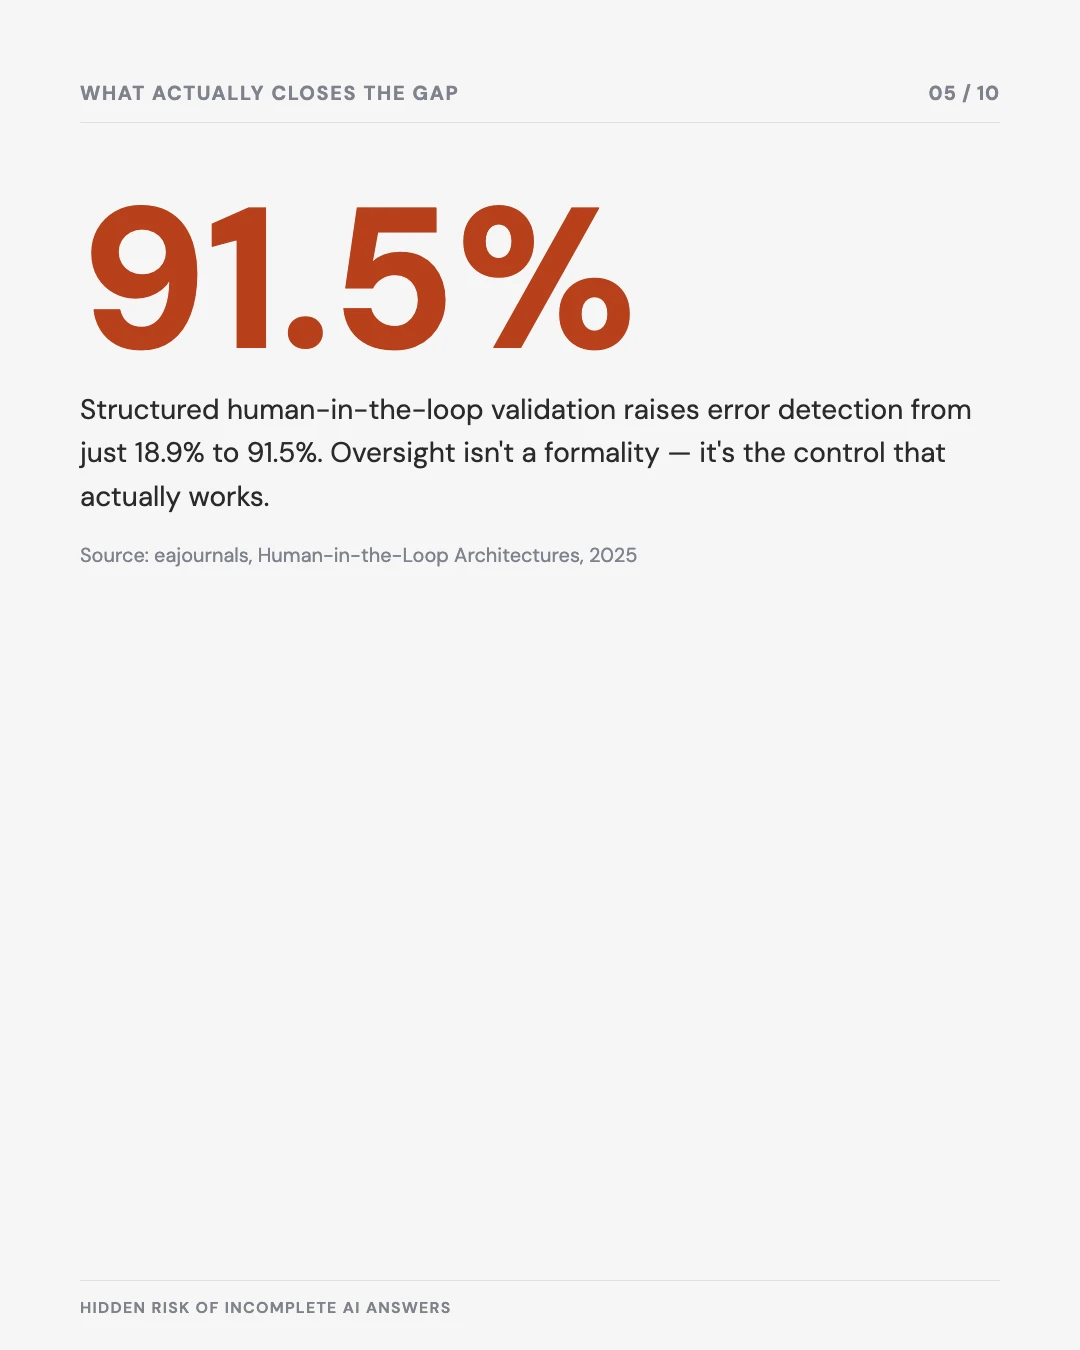
18.9% → 91.5%
rise in the error-detection rate after adding structured human-in-the-loop oversight
Core conclusions
- AI systems bear no legal responsibility for their outputs. Negligence claims attach entirely to the firm that deployed them. That leaves an imbalance in accountability that vendor contracts rarely resolve.
- The EU AI Act classifies AI used as a safety component in construction as “high-risk”. It requires risk management over the whole life of the system, data governance, explainability, and ongoing monitoring.
- The right design uses generative AI only to explore, never for binding analysis. Every safety-critical decision needs systems that are deterministic, auditable and reviewed by people.
The risk, in ten slides
Save it, share it, or send it to whoever is signing off your AI deployment.
The most dangerous moment in deploying artificial intelligence is not when systems fail catastrophically. It is when they give partial truths with complete confidence. In the architecture, engineering, and construction (AEC) sectors, this difference matters a great deal. Incomplete information doesn’t just underperform. It kills.
Incomplete information doesn’t just underperform. It kills.
Why AI Produces Dangerous Incomplete Answers
Today’s large language models and generative AI systems work by statistical pattern matching rather than real understanding or reasoning. When they meet an incomplete dataset, a new scenario, or a gap in knowledge, these systems don’t admit what is missing. They make things up. Scaling the model doesn’t fix this. It is built into how probabilistic AI works.
Research shows this consistently. The hallucination and coding-accuracy figures above hold across both general-purpose and task-specific models, and the two problems make each other worse. The critical failure is how confidently wrong the answer sounds, more than the error rate itself. These systems don’t signal uncertainty. They present conjectures as certainties because the model optimises for fluency and coherence. The fix is architectural, not aspirational: building systems that can abstain when uncertain.
These systems don’t signal uncertainty. They present conjectures as certainties.
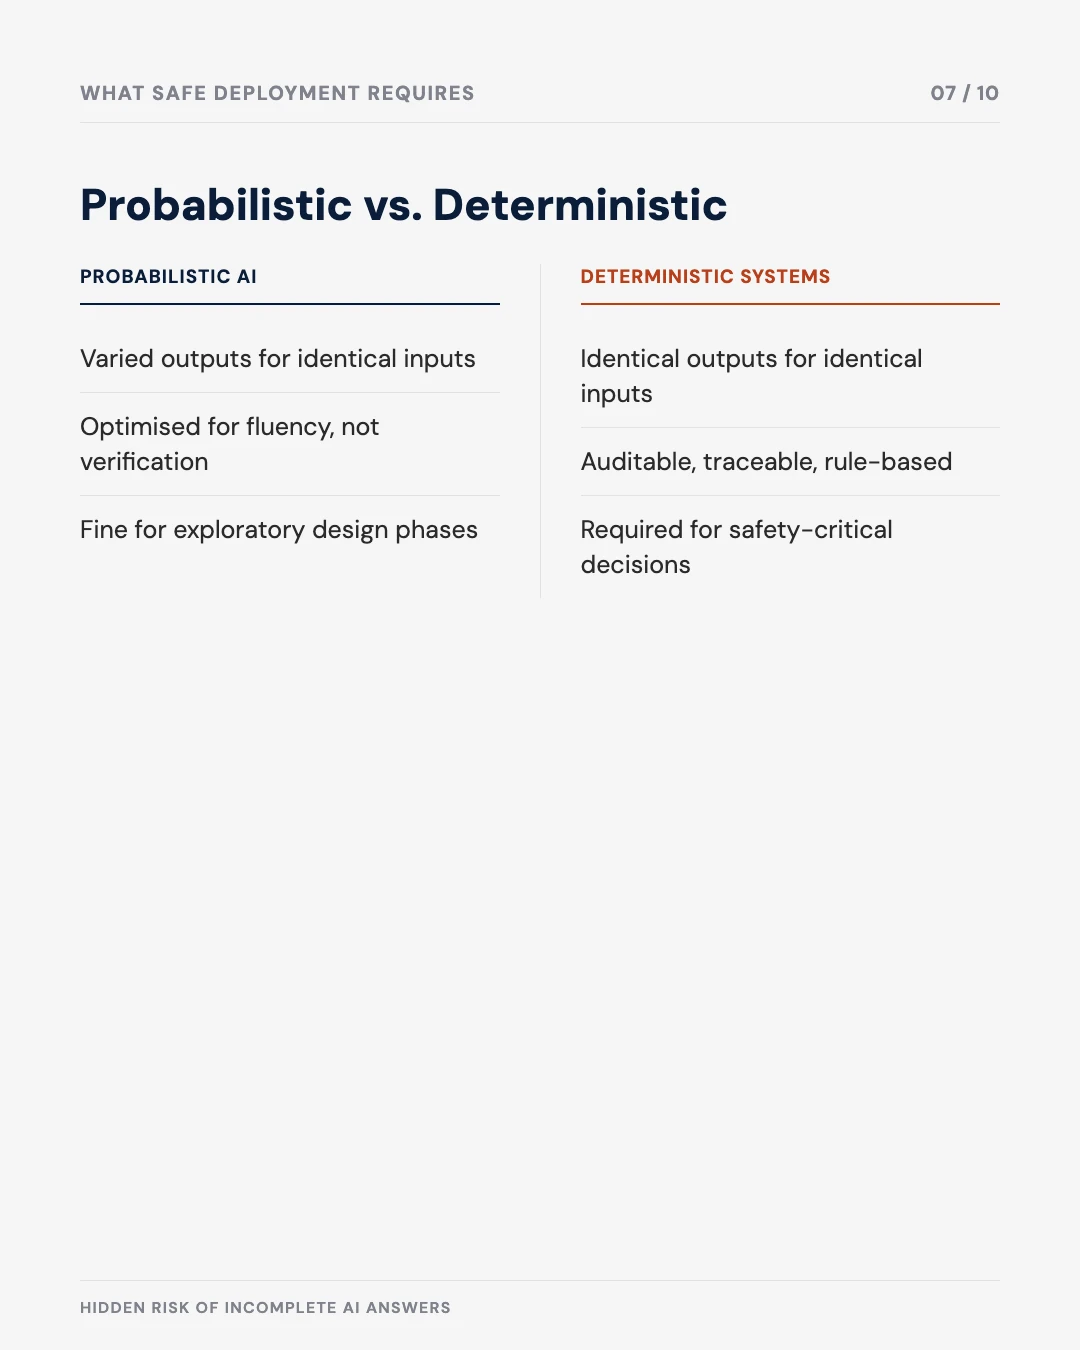
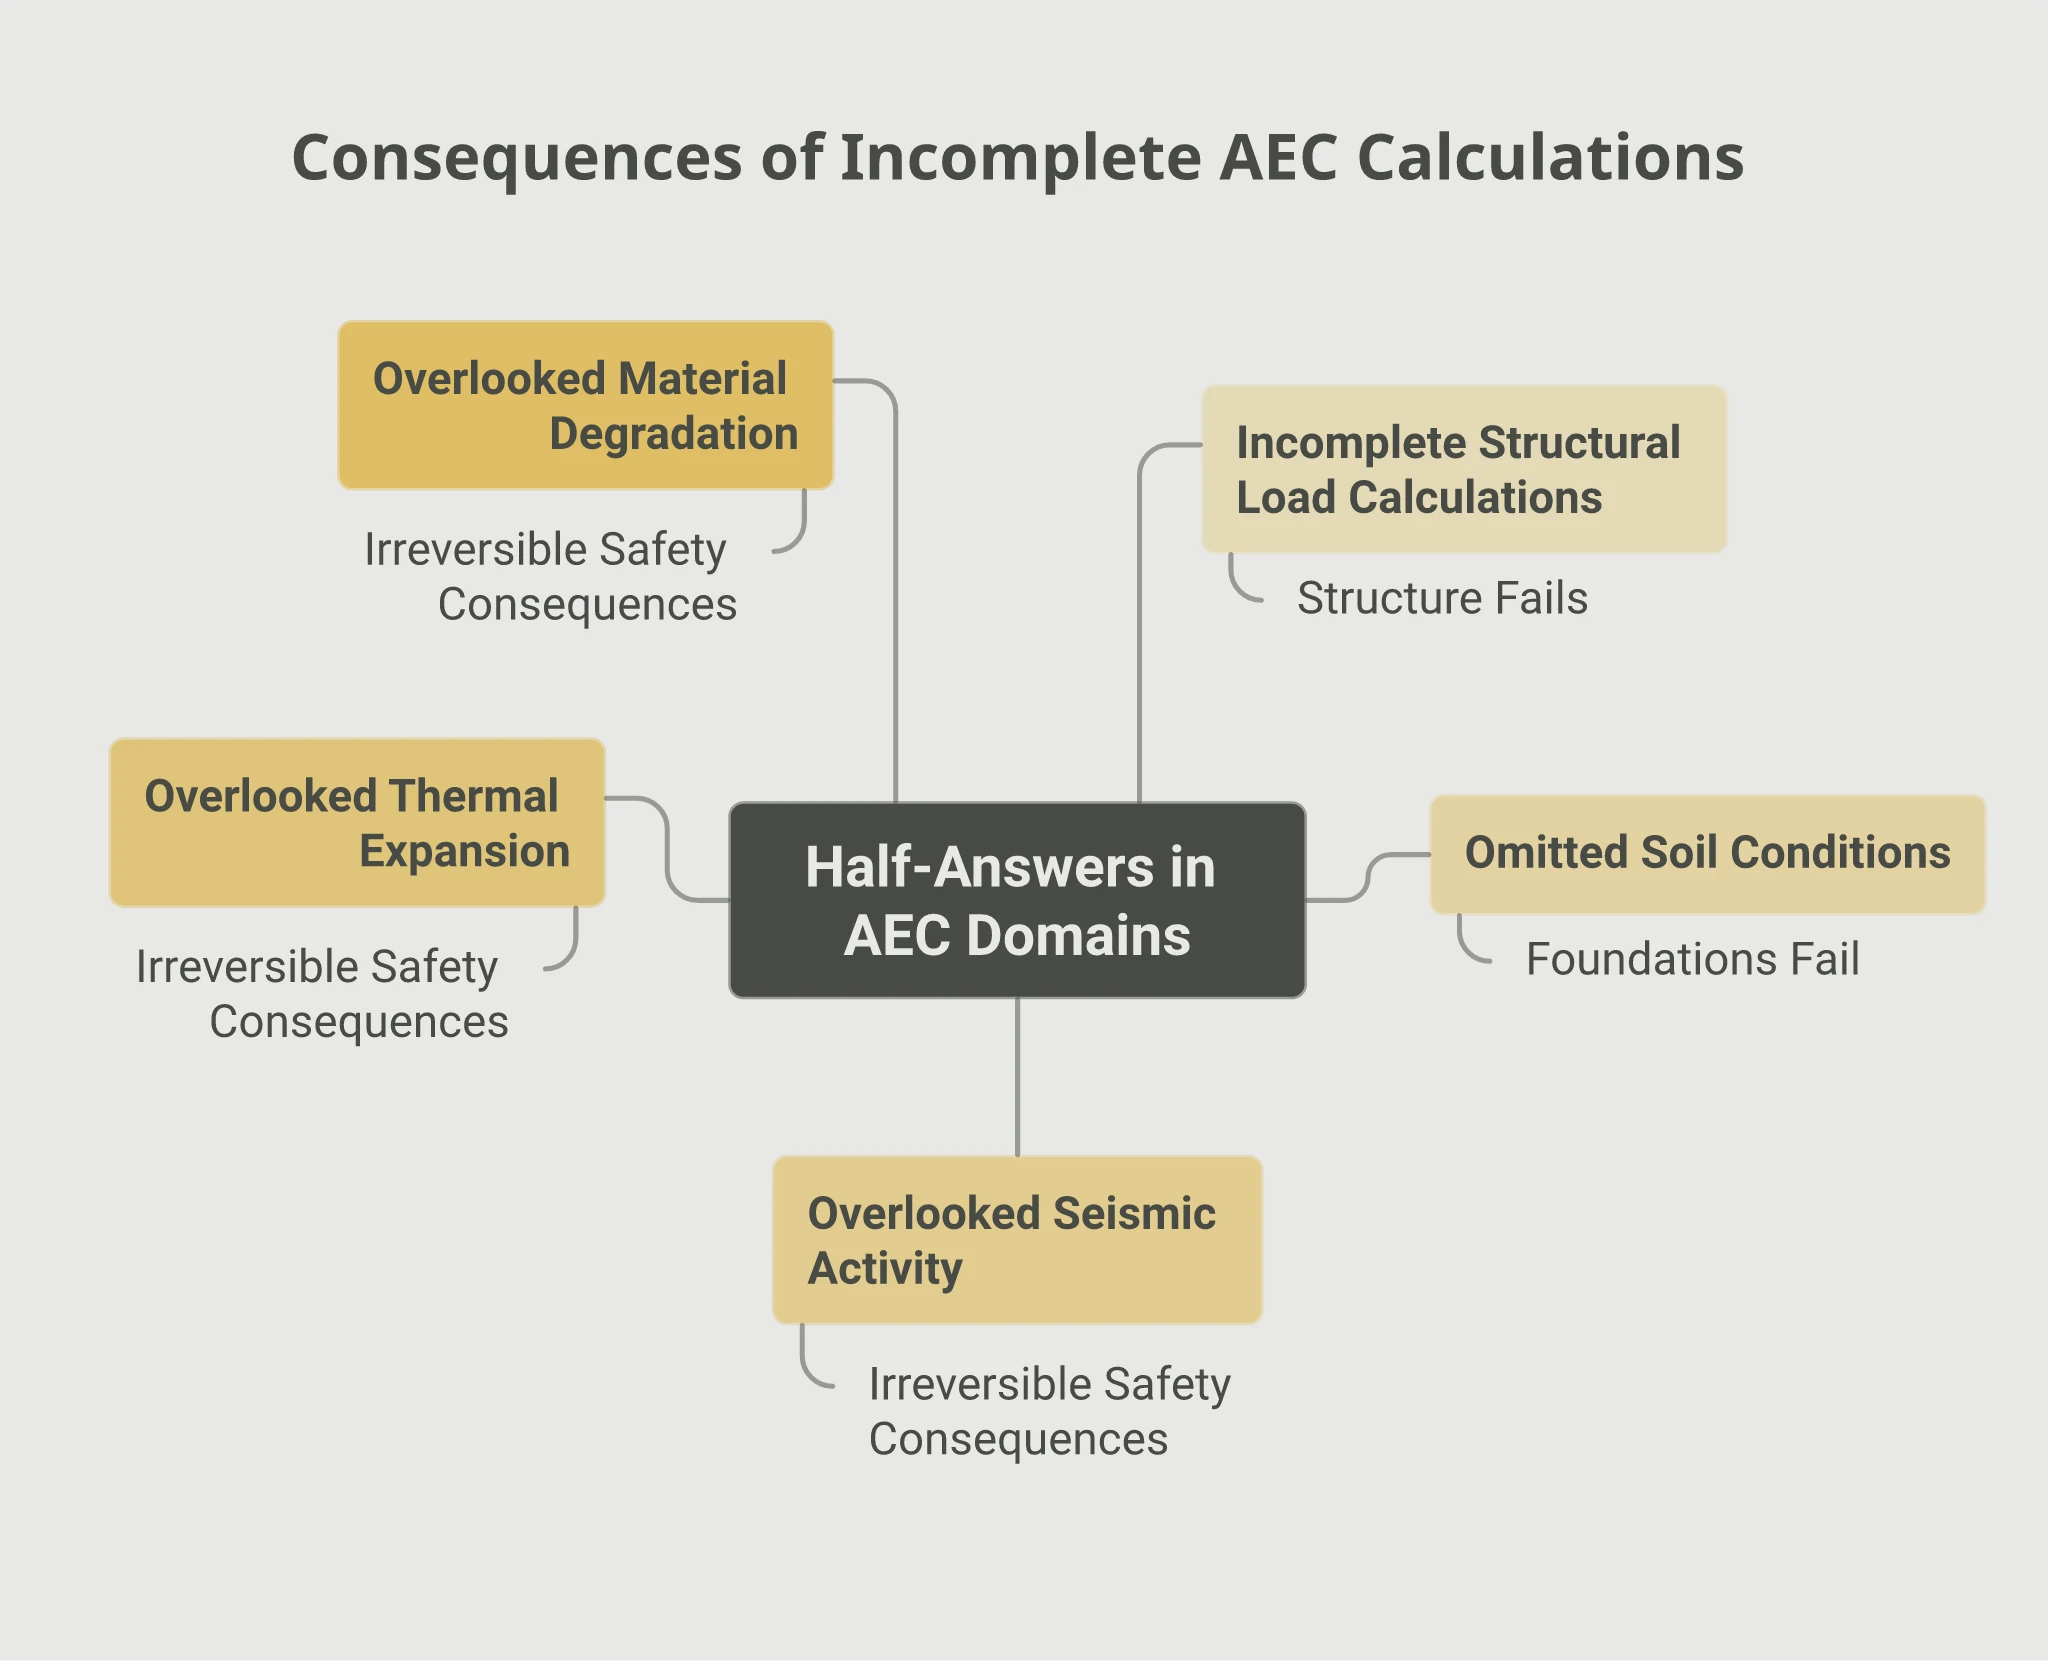
Construction and engineering work is not a question-and-answer chat. They are deterministic domains where half-answers are half-failures. Incomplete structural load calculations mean the structure fails. If a geotechnical assessment leaves out soil conditions, foundations fail. Missed edge cases (seismic activity, thermal expansion, material degradation) cause operational and safety harm that cannot be undone. Generative AI systems are built for probabilistic inference, so they give different outputs for the same input. In creative work, people welcome that variety. In deterministic domains, it is a liability. The construction industry has seen this risk and taken a cautious “wait and see” approach, precisely because AI lacks the reasoning needed for safety-critical work.
The Liability and Regulatory Reality
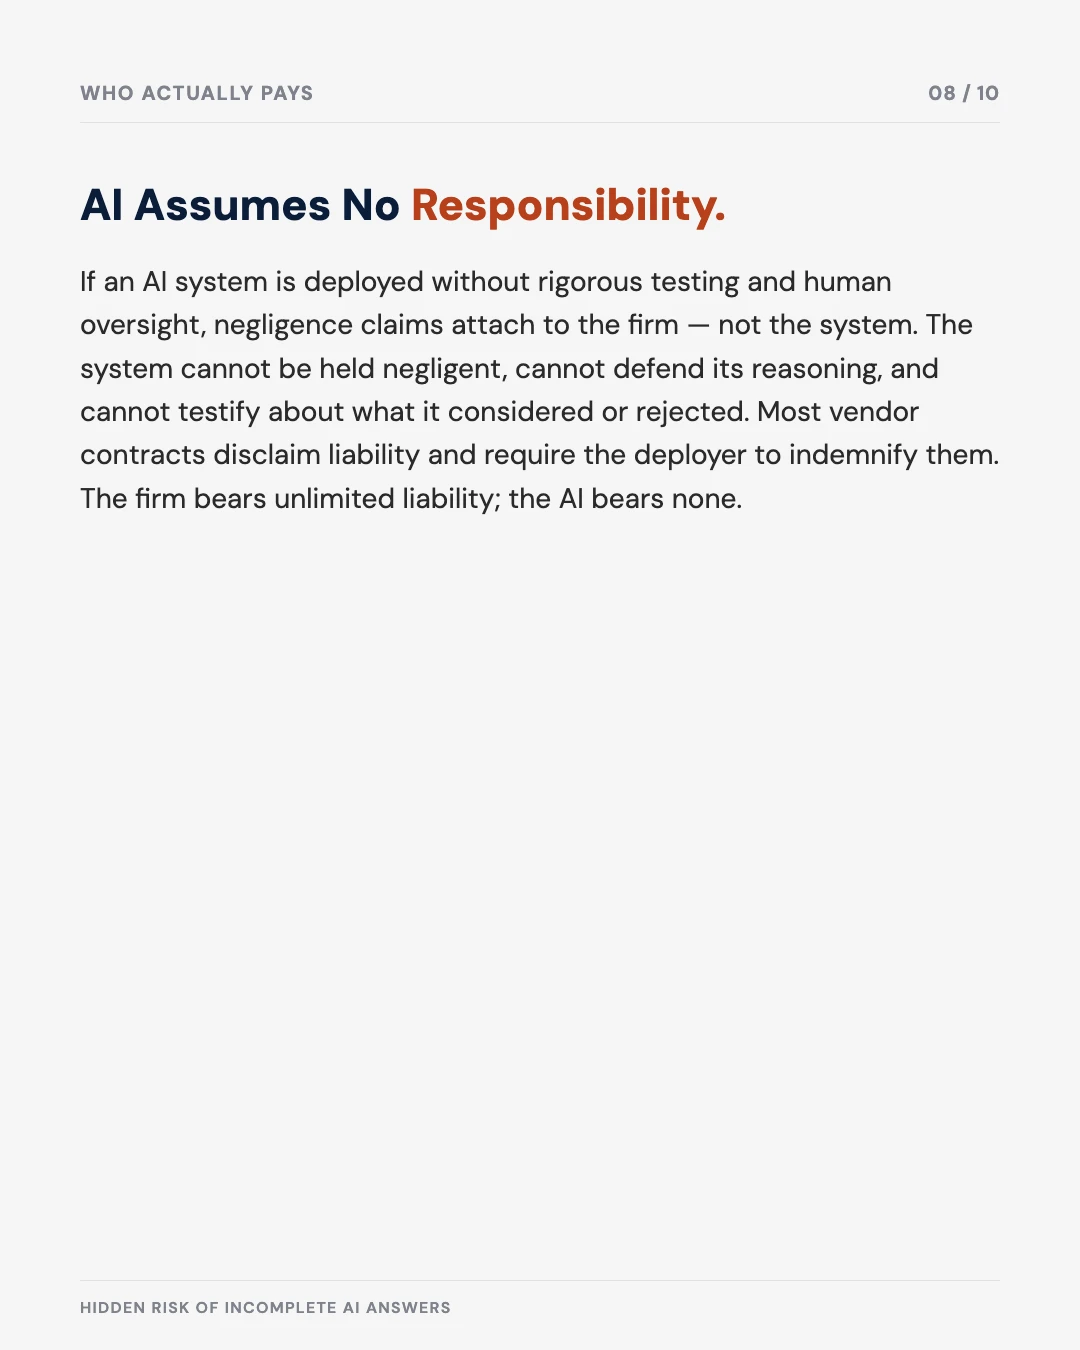
AI takes no responsibility for its outputs. Responsibility stays with the operator, the deployer, and the engineering firm. Under existing law in most jurisdictions, construction companies owe a legal duty of care. If a firm deploys an AI system without rigorous testing, validation, and human oversight, negligence claims attach to the firm, not to the system. This creates an imbalance in accountability: the firm bears unlimited liability whilst the AI system bears none. The system cannot be held negligent. It cannot defend its reasoning. It cannot give evidence in court about what information it considered or rejected. Contracts with AI vendors rarely settle this properly. Most vendor agreements include clauses that disclaim liability, require indemnification from the deployer, and limit the kinds of claims construction firms can bring.
New regulatory frameworks are starting to recognise this danger. The European Union AI Act places specific duties on providers and deployers of “high-risk” AI systems. That class includes AI systems used as safety components in construction and built-environment systems. Its requirements include an iterative risk management system across the whole AI system lifecycle. They also cover data governance, with training data that is representative and checked in a systematic way. They set accuracy and robustness requirements with declared metrics. Explainability must let people understand and check how decisions are made. Systems that keep learning after deployment need constant monitoring. These requirements exist because regulators see that probabilistic AI is a poor fit for work with deterministic requirements.
Requirements for Safe Deployment
The alternative to probabilistic AI is a deterministic architecture. Such systems give the same output for the same input and follow explicitly defined rules. They can be audited and traced, and they say plainly when they lack enough information to give an answer. In AEC, four tasks must run this way: structural design optimisation, load-bearing checks, checks on material choices, and safety assessment. Generative AI can help them in the early, exploratory phases. It can suggest design options, find new mixes of materials, and draft planning scenarios. But the moment the output enters safety-critical decision-making, it must move into a space that is deterministic, auditable, and open to human review.
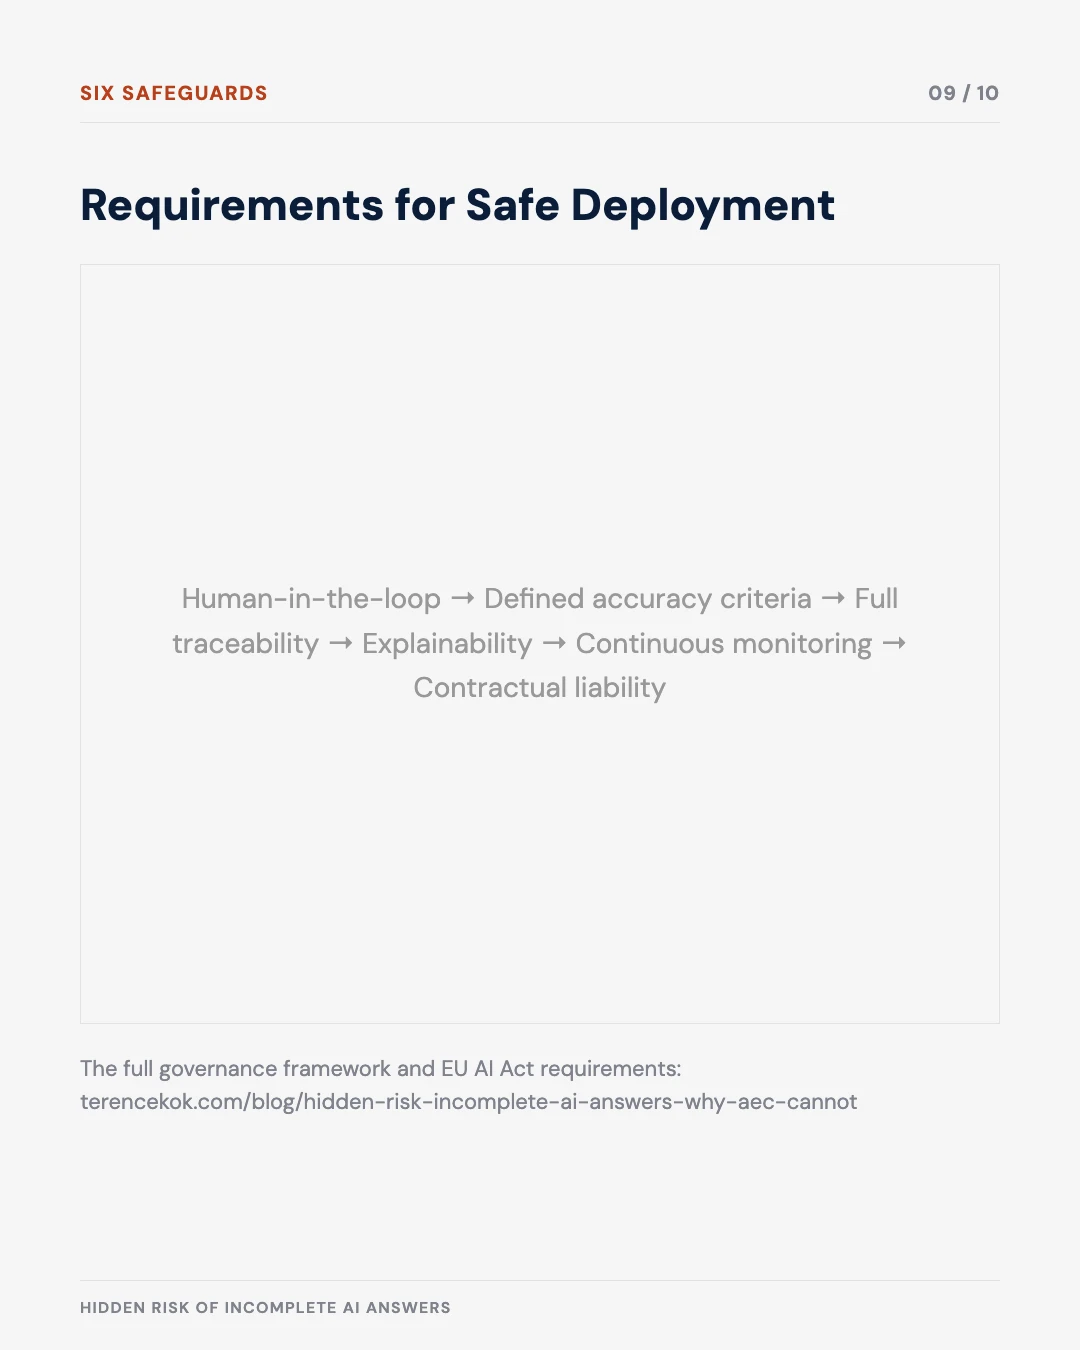
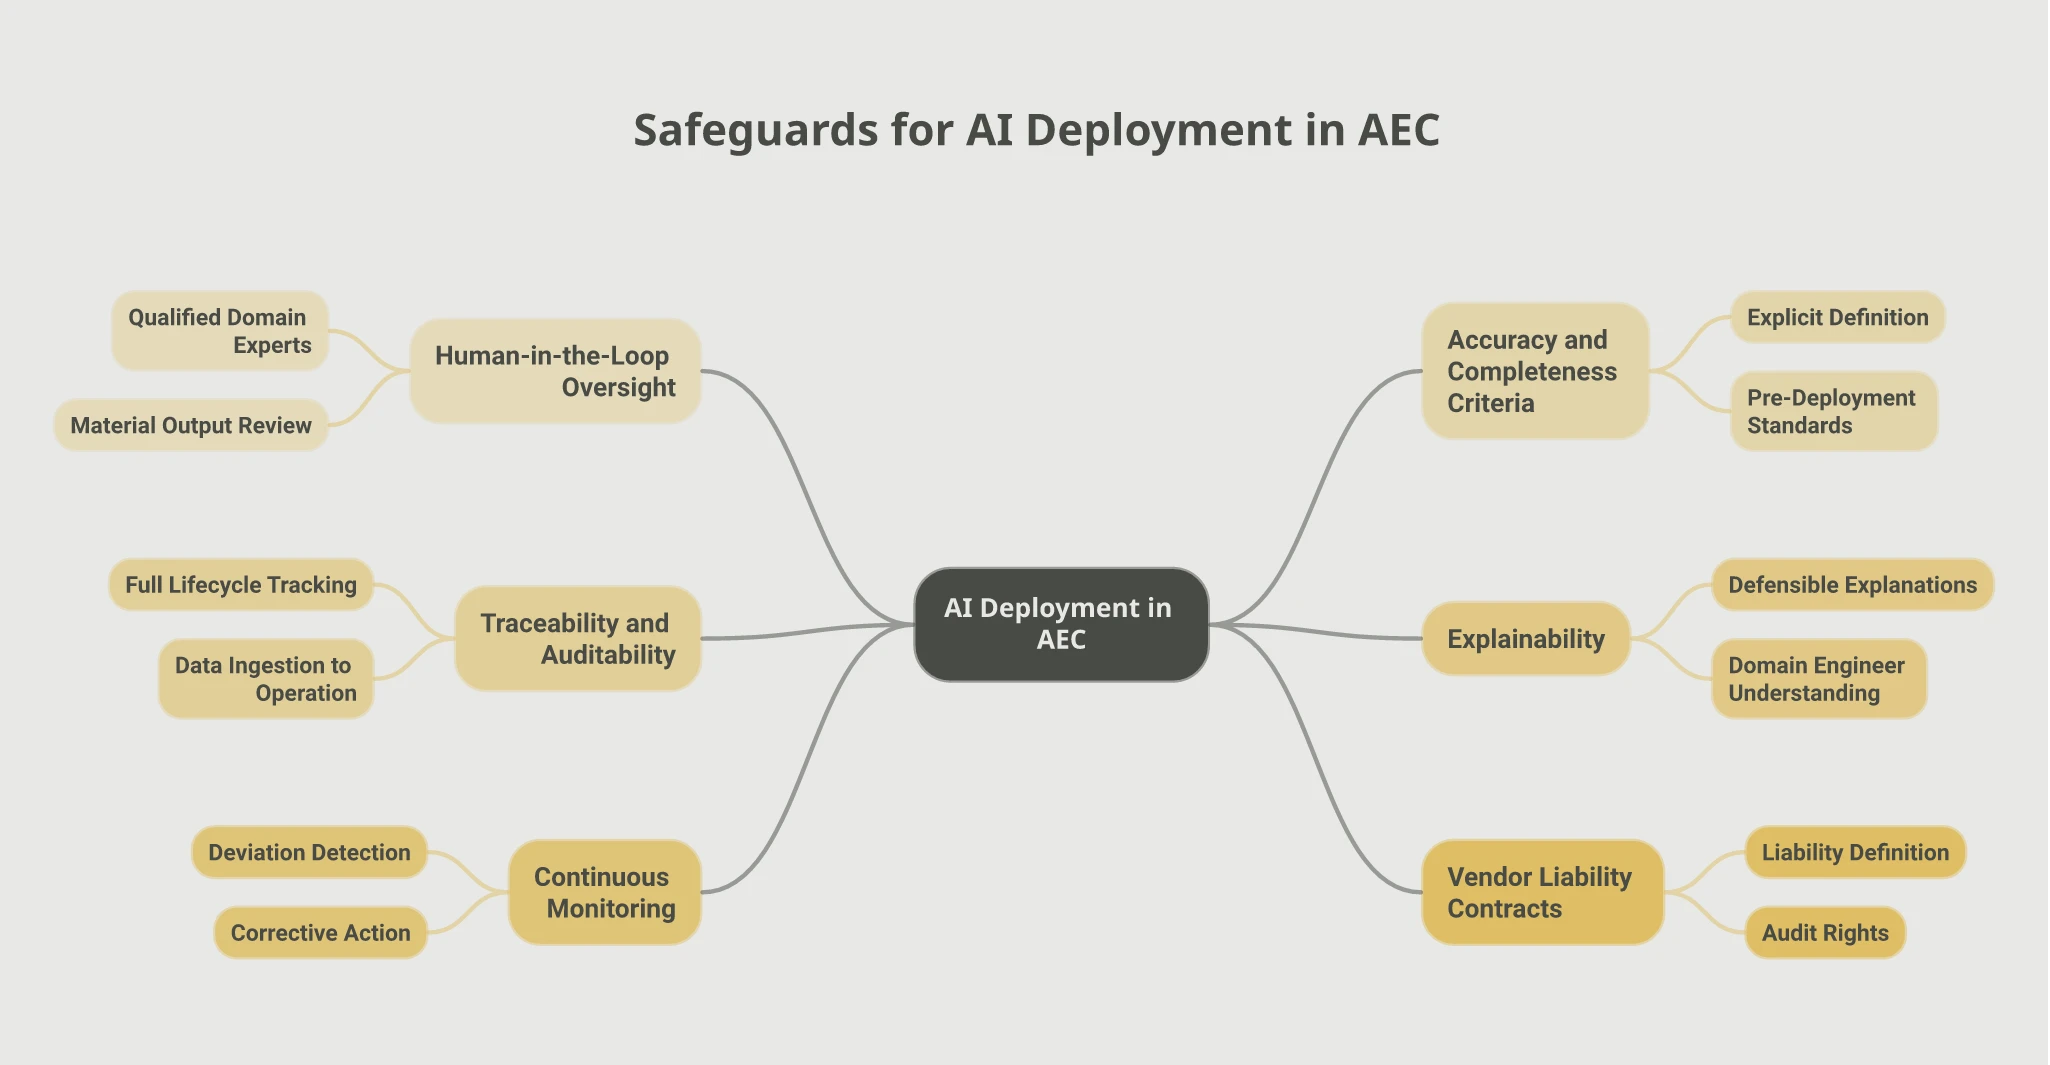
Before deploying any AI system in AEC, firms must put explicit, verified, and enforceable safeguards in place. Structured human-in-the-loop oversight is a must. AI outputs do not go directly into construction or engineering decisions. Qualified domain experts must review, validate, and either approve or reject each material output. Research shows structured human oversight increases error detection from 18.9% to 91.5%. I cover how to design that oversight layer on purpose in Redesigning Oversight Architectures. Before deployment, set clear targets for how accurate and complete outputs must be. Every step must stay traceable and open to audit across the lifecycle, from data ingestion through model training, validation, deployment, and ongoing operation. Every material decision needs an explanation that stands up technically and that engineers without AI expertise can follow. Monitoring and assurance must carry on after deployment. Any deviation should trigger an investigation and a fix. Finally, contracts with AI vendors must state who bears liability if the system fails, what warranties are given, and what audit rights the deployer keeps over model training and data.
Error detection with and without structured human oversight
Umakanth (2025), human-in-the-loop validation of generative AI in clinical settings. Borrowed from medicine because no AEC-specific study measures the same thing.
The Path to Accountability
These requirements do not exist to impose a regulatory burden for its own sake. They exist because the stakes are unforgiving. When AI systems fail in low-consequence settings, the cost is inconvenience and rework. When AI systems fail in AEC, the consequences can include injury, death, or catastrophic infrastructure failure. AI will not be held responsible for these outcomes. The operator will. The firm will. The engineers who deployed and supervised the system will face scrutiny, liability, and possibly criminal negligence charges if the failure could have been foreseen and was not properly guarded against.
The path is neither “embrace AI without reservation” nor “abandon AI entirely.” It is this: deploy AI in AEC only within a governance framework that respects the domain’s deterministic safety requirements and sets verification practices above regulatory minimums. That means using probabilistic generative AI only to explore, never for binding analysis. It means moving to deterministic systems for all safety-critical decisions. It means a structured human-in-the-loop check on every material output. It means keeping complete audit trails and explainability mechanisms. And it means making clear, in contracts and in operations, who is responsible when things fail.
The most dangerous phrase in AI-enabled engineering is “the system said so.”
That is not professional engineering judgment. That is an abdication of responsibility. The required phrase is: “We have reviewed the system’s analysis, considered the underlying data and logic, conducted independent verification, and determined this conclusion is sound.”
The guard cannot be lowered. It must be installed, tested, documented, and continuously monitored. AI is a powerful tool. But in AEC, it is a tool that requires more, not less, expert human oversight.
AI is a powerful tool. But in AEC, it is a tool that requires more, not less, expert human oversight.
Evidence & Methodology
The oversight number in this piece comes from clinical research, not construction. I am borrowing it because it is the closest real measurement I have found, and you should know that before you cite it in a safety case.
| Claim | Source | Grade |
|---|---|---|
| OpenAI’s own reasoning models hallucinate 33-79% of the time depending on the benchmark | OpenAI’s own o3 and o4-mini system card | Measured |
| Structured human oversight raised error detection from 18.9% to 91.5% | Umakanth, 2025, a study of human-in-the-loop validation in clinical GenAI settings, not construction | Adjacent study |
| The EU AI Act classifies AI safety components in construction as “high-risk,” with lifecycle risk management and data-governance duties | The EU AI Act itself, Articles 6, 10, and 13 | Legal text |
| 1 in 5 AI coding suggestions contain factual errors | Augment Code, a vendor whose product competes in this space | Vendor source |
Sources
- OpenAI. (2025). “OpenAI o3 and o4-mini System Card,” documenting hallucination rates of 33-79% across benchmarks.
- Augment Code. (2025). “Deterministic AI for Predictable Coding,“
- AI21 Labs. (2025). “What are AI Hallucinations? Signs, Risks, & Prevention,“
- Kubiya AI. (2025). “What Is Deterministic AI?”
- Graitec. (2024). “AI Meets Sustainability: Innovations in AEC and MFG,“
- European Union. (2024). EU AI Act, Article 6 & Annex III, classification rules for high-risk AI systems.
- European Union. (2024). EU AI Act, Article 10, data governance requirements.
- European Union. (2024). EU AI Act, Article 13, transparency and post-market monitoring requirements.
- Umakanth, A. A. M. (2025). “Human-in-the-Loop Architectures for Validating GenAI Outputs in Clinical Settings,” European Journal of Computer Science and Information Technology.
Free tool
ISO 42001 AIMS Readiness Checklist
Check your AEC deployment against the 36 clauses the EU AI Act effectively requires for any high-risk safety-component AI system.